Mapping attributes and the organizational structure
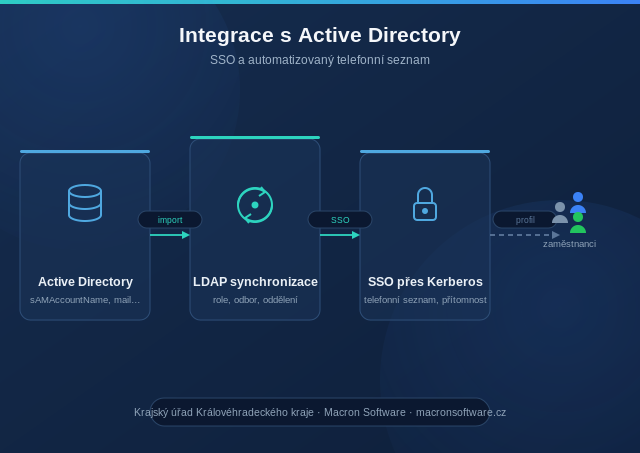
The attribute mapping covers sAMAccountName, mail, givenName, sn, telephoneNumber, and mobile. The department and the unit are derived by parsing distinguishedName.
Authentication separated from authorization
Authorization is kept separate from authentication: the default role is employee, and higher roles are assigned manually.
Single sign-on through Kerberos
For the convenience of users, single sign-on was implemented using Kerberos and the LDAP SSO module.
An automated phone directory
The phone directory is generated from user entities and controlled by a display flag. Photographs are synchronized from an external directory by personnel number, and a dedicated role is required to see them.
Presence status tied to the attendance system
Presence status is connected to the internal attendance system database and refreshed periodically.
The solution keeps administrative overhead to a minimum and centralizes identity management.
Series: Hradec Králové Region Civil Servant Portal